Protecting Your Private Information
We employ the highest industry recognized security safeguards to help protect the personally identifiable information that you have provided to us from loss, misuse, or unauthorized alteration. Digital threats continue to grow more sophisticated daily. Regal Home Lending understands these risks and proactively enforces company policies and procedures along with third party security measures to protect your private information.
- Secure Website Connection (TLS): The Regal Home Lending website is secured with Transport Layer Security (TLS), the modern successor to SSL. Our server supports only the current TLS 1.3 and TLS 1.2 protocols, and older, less secure protocols (SSL 2.0, SSL 3.0, TLS 1.0 and TLS 1.1) are disabled. Information passed between your browser and our website is encrypted so it stays confidential.
- 256-Bit Encryption: Our server prefers 256-bit encryption, including AES-256, the same cipher the NSA has approved for protecting TOP SECRET information. Every connection also uses forward secrecy, which means each session is protected by its own temporary keys, so past sessions stay protected even if a key were ever compromised.
- File Handling: All company email and file storage is hosted on Google Workspace, one of the most secure business platforms available. Google encrypts your data when it is stored on disk, stored on backup media, moving over the Internet, and traveling between Google data centers.
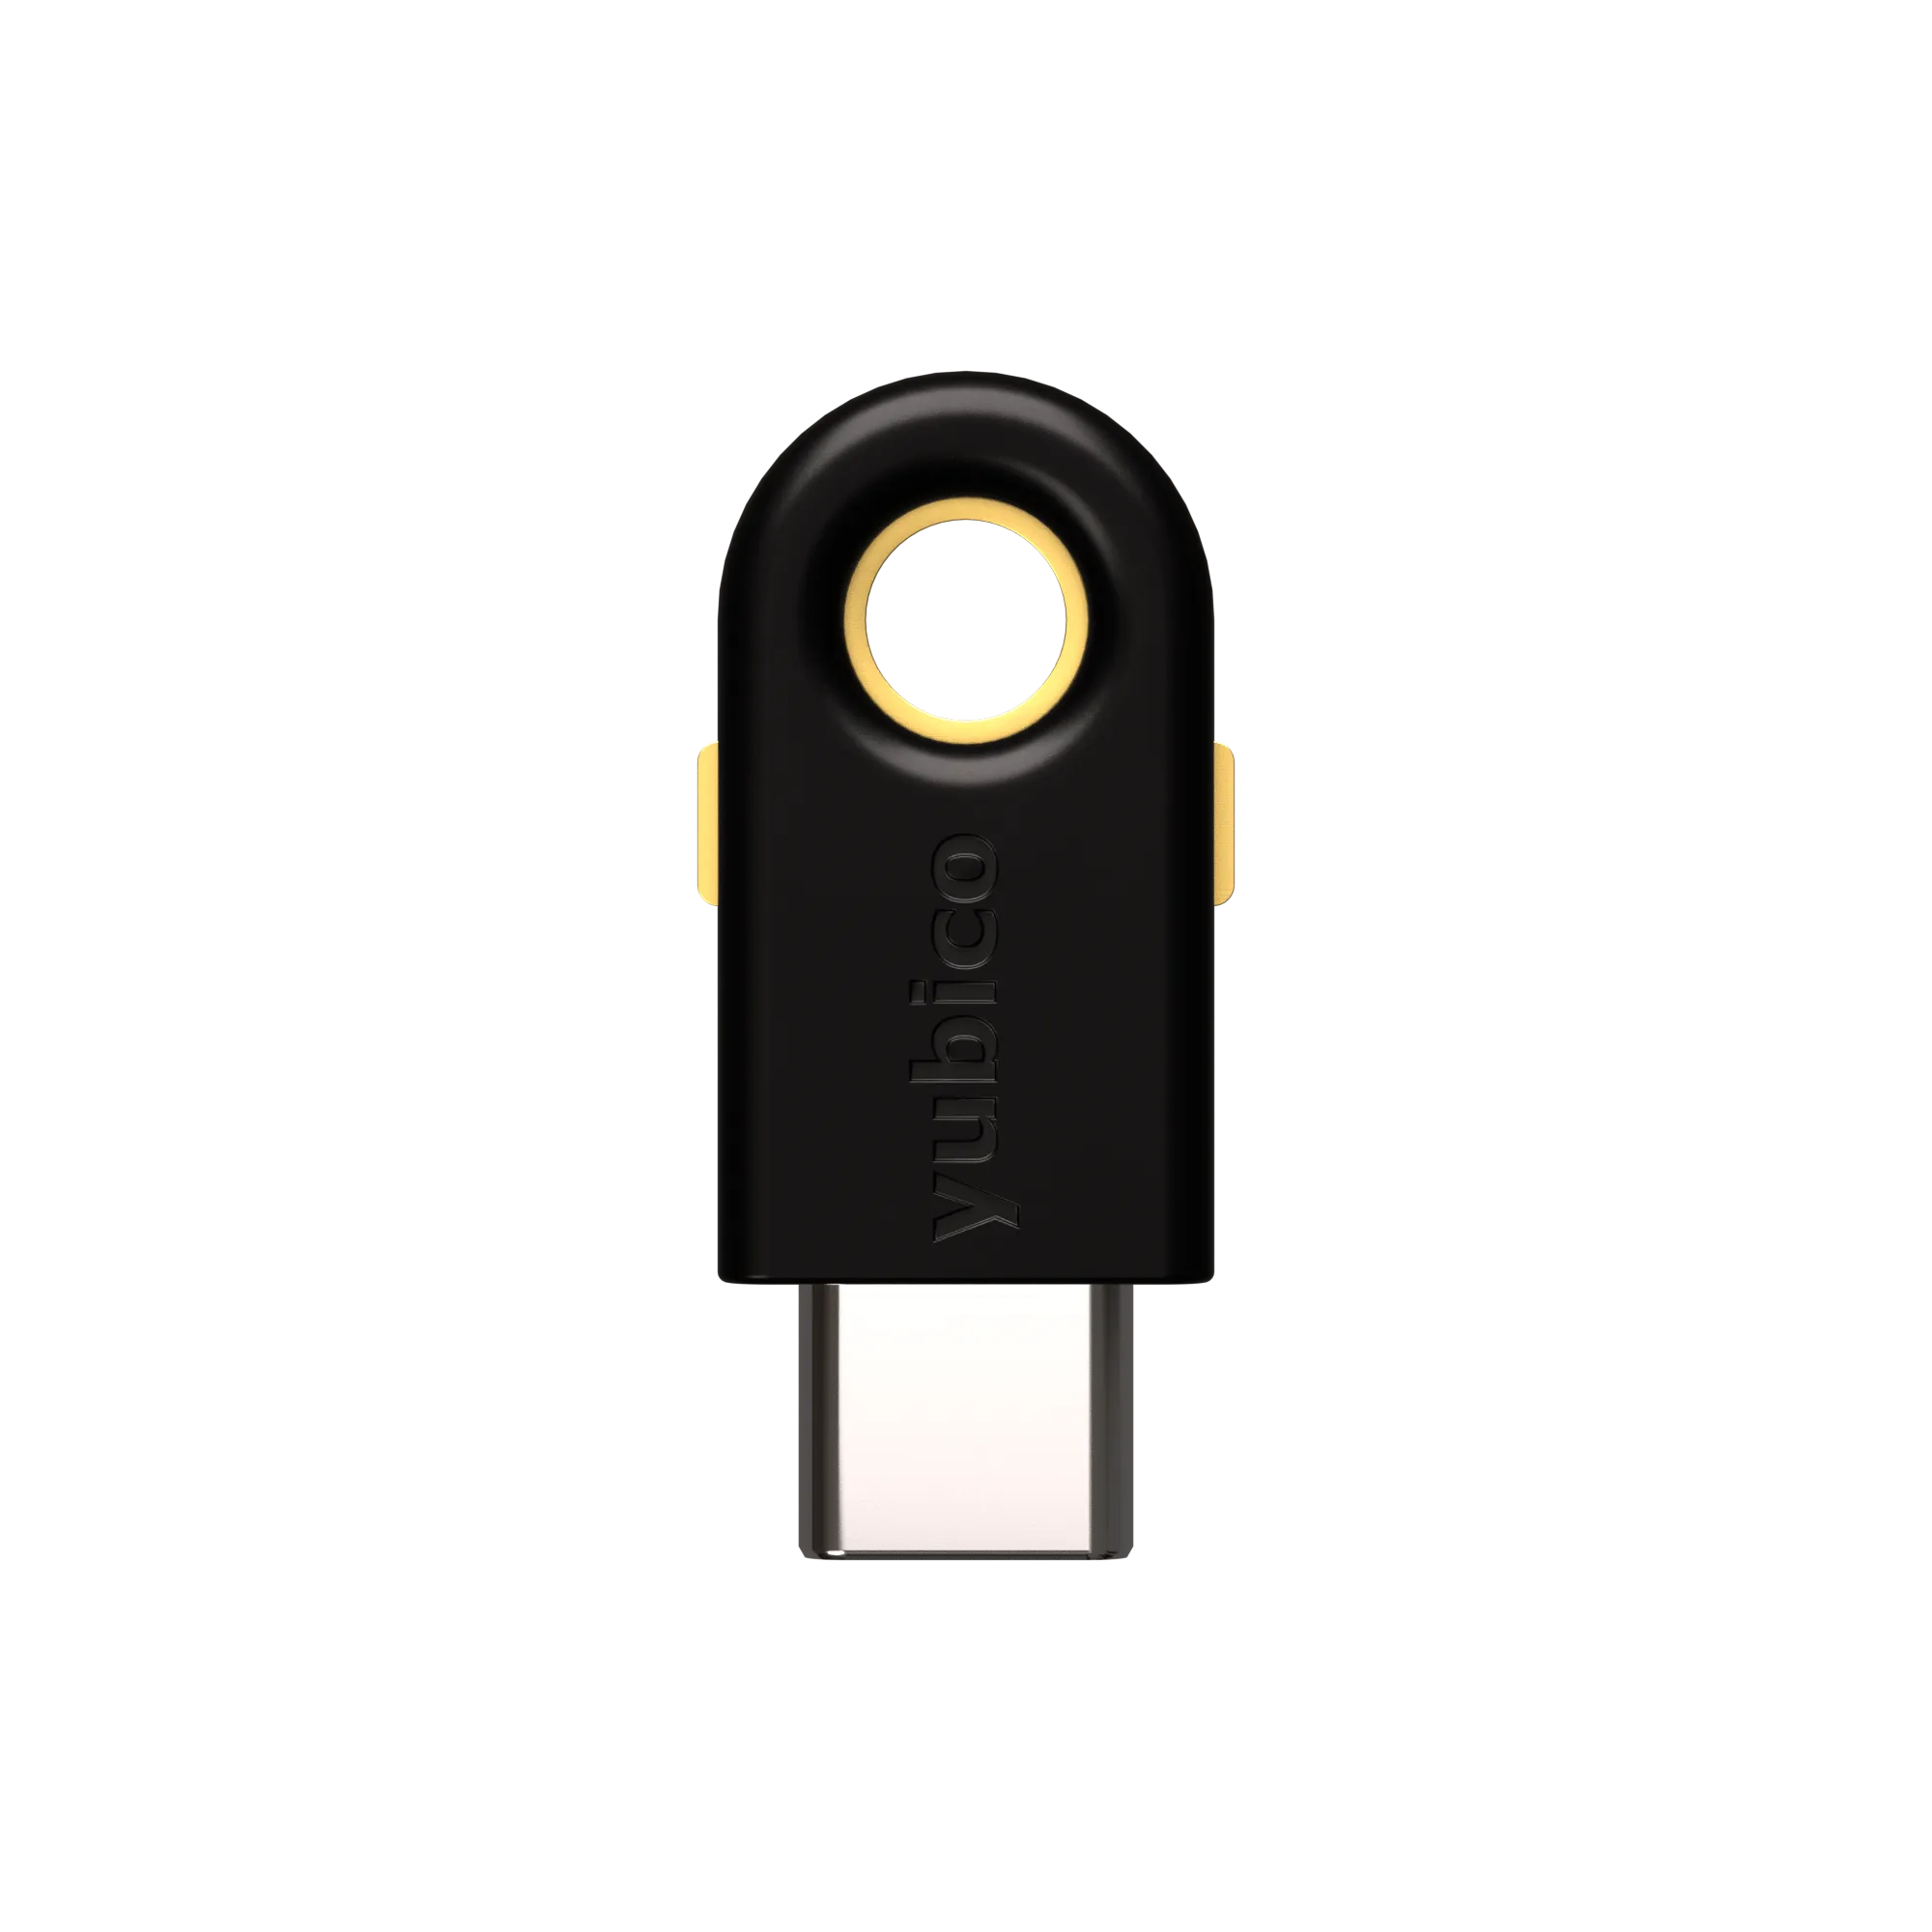
- Hardware Security Keys (YubiKey 5C FIPS): Regal Home Lending team members sign in to company systems with the YubiKey 5C FIPS, a physical hardware security key built to meet U.S. federal government security requirements. Instead of a text message or one-time code that can be intercepted, the key performs a cryptographic handshake using the FIDO2/WebAuthn standard that is bound to the real website, so a fake login page cannot trick it. Even if a password were ever stolen, no one could access our systems without physically holding the key.
- Government-Grade Protection: The YubiKey 5C FIPS was validated under the U.S. government’s FIPS 140-2 cryptographic standard (Overall Level 2, Physical Security Level 3), is FIDO2 Level 2 certified, and meets the highest authenticator assurance level (AAL3) defined by NIST. It supports the same encryption standards (AES-256 and ECC P-384) the NSA has approved for protecting TOP SECRET information. Its credentials are created and stored on a tamper-resistant secure element and are designed so they cannot be copied or extracted. Manufactured in Sweden and programmed in the USA, it requires no battery or network connection, and is water resistant (IP68) and crush resistant.